G+D Netcetera manages 1.4 billion tokens
Payment tokenization as prerequisite in e-commerce

Reduce risk for non-authenticated transactions, associated refunds, and lost revenue.
Establish frictionless flow and improve the cardholder experience during online shopping.
As digital payment systems become more interconnected, their vulnerability grows. The 3DS Server is built to evolve with that landscape.

Certified against PCI 3DS, PCI DSS and all major card schemes and many local schemes. Hosted on G+D Netcetera's Cloud Payment Platform, with regular updates and upgrades.
Admin UI for data configuration, transaction search, reports, and user access management. Test environment. Easy API integration. 24/7 online customer support.

Fast and easy integration via comprehensive technical documentation, guidance webinars, and professional G+D Netcetera support.
Compliant with Visa, Mastercard, American Express, JCB, Discover/Diners, Cartes Bancaires, UnionPay, Eftpos, Dankort, Jaywan, Elo.

G+D Netcetera’s PCI 3DS certification already covers the authentication components you depend on.
When card networks or regulators ask for proof of compliance, you point to G+D Netcetera's certification reports rather than running separate assessments.

G+D Netcetera is an official member of the AWS Partner Network.
The 3DS Server SaaS operates on AWS infrastructure, supporting high availability, elasticity, and operational resilience at any transaction volume, from individual merchants to large acquirer portfolios managing thousands of merchants.
The G+D Netcetera 3DS Server was the first product approved by EMVCo in Europe and the second in the world. Fully compliant with the EMV 3DS 2.x protocol and all major card scheme EMV 3DS 2.x programs. This is not a legacy product retrofitted for 3DS 2.x. It was purpose-built for the specification from the outset — and has been updated through every subsequent version since.
A single 3DS Server deployment supports configuration for multiple acquirers, merchants, and PSPs, within a single integration. Payment platforms managing large and diverse merchant portfolios can extend consistent, standards-based authentication across every client on a single infrastructure investment. Acquirers can cover smaller merchants with the same high-quality authentication as their largest clients.
A JavaScript Web SDK is included for invoking 3DS Method, Challenge and SPC request messages in browser-based transactions.
Merchants do not need to build their own browser-side authentication logic — the SDK handles it. Combined with the server-side 3DS Server, this is a complete client-server EMV 3DS implementation in a single integration project.
SaaS: Admin UI covering data configuration, transaction search and report creation, and user access management.
Full operational visibility built into the product across both deployment models.
SaaS: a simulated Directory Server and ACS for integration testing — no waiting for scheme test environment availability.
On-premise: the NDM Simulator provides a full test application with a demo web shop, Directory Server, and ACS. Both paths provide integration testing that mirrors production conditions.


EMV 3DS authentication happens entirely within the merchant environment. No disruptive redirects, nor handoffs to separate authentication pages. The cardholder stays in the checkout throughout.

The vast majority of genuine transactions complete without any step-up required. The cardholder taps pay, the authentication runs invisibly in the background, and the purchase completes. That is the right experience for customers who have done nothing wrong.

When a challenge is required, it is proportionate and fast — via biometrics, one-time password, or device recognition. Compliant with EMV 3DS programs and certified with: Visa, Mastercard, American Express, JCB, Discover/Diners, Cartes Bancaires, UnionPay, Eftpos, Dankort, Jaywan, Elo.
Security and user experience are not competing priorities but complementary elements of a successful digital strategy. As payment systems become more interconnected, their vulnerability to sophisticated cyberattacks grows. Companies cannot navigate this alone — and they should not have to."

A 3DS Server is the component on the acquirer or PSP side that initiates and manages the EMV 3DS authentication flow for card-not-present transactions. It communicates with the card scheme's Directory Server and the issuer's ACS to authenticate the cardholder before a payment is processed. PSPs and acquirers need a 3DS Server to meet Strong Customer Authentication requirements, reduce fraud risk for non-authenticated transactions, shift liability for fraudulent transactions to the issuer, and — critically — to do all of this without unnecessary friction on genuine transactions. How well the Server sends authentication data determines how many of your customers are challenged unnecessarily.
Three things that are hard to replicate: provenance (first EMVCo-approved product in Europe, second globally — built from the specification's foundation, not retrofitted for it), breadth (10+ scheme certifications with publicly available Letters of Attestation for each), and integration depth (G+D Netcetera also builds the ACS and Directory Server the 3DS Server communicates with, so testing is against real counterparts, not simulated proxies). The Juniper Research RegTech Gold award is external validation of that track record.
SaaS: API integration into your existing payment environment. A JavaScript Web SDK handles browser-side 3DS Method, Challenge and SPC Request messages. A simulated Directory Server and ACS are available for integration testing. Full technical documentation is available at 3dss.netcetera.com/3dsserver-saas/doc/current. Dedicated team to support the onboarding process. 24/7 customer support is included.
G+D Netcetera's PCI 3DS certification covers the operated authentication components. When card networks or regulators ask for proof of compliance, you point to G+D Netcetera's certification reports rather than running separate assessments. G+D Netcetera manages the certification process with the schemes — without requiring customer involvement for most of them.
Integration documentation for SaaS and on-premise deployments and API references. Both deployment paths, fully documented.
The mobile companion to the 3DS Server. Handles in-app authentication for native mobile payment flows — the same PCI-certified, scheme-compliant quality extended to every channel where your customers shop.
Click to Pay handles payee recognition and token-based card presentation. The 3DS Server handles authentication. Together they cover the full checkout security stack for merchants and PSPs.
The issuer-side complement to the 3DS Server. G+D Netcetera provides both ends of the authentication conversation from a single partner — built and tested together, no integration surprises between components.
Network tokenization and 3DS authentication address different problems but reinforce each other. The eCOM Tokenizer gives merchants access to major card network token services through a single connection — pair with the 3DS Server for a complete e-commerce security layer.
Payment tokenization as prerequisite in e-commerce
First-party misuse is now the world’s leading type of fraud, yet it is almost impossible to spot at checkout. Discover why friendly fraud is rising, what it costs the payments industry, and how better data sharing could help distinguish genuine disputes from deliberate abuse.
G+D Netcetera wins two Juniper Awards 2026 for fraud prevention and digital wallets, as banks rethink their systems landscape for future payments
3DS and SCA are working as designed. So why is UK payment fraud still rising?
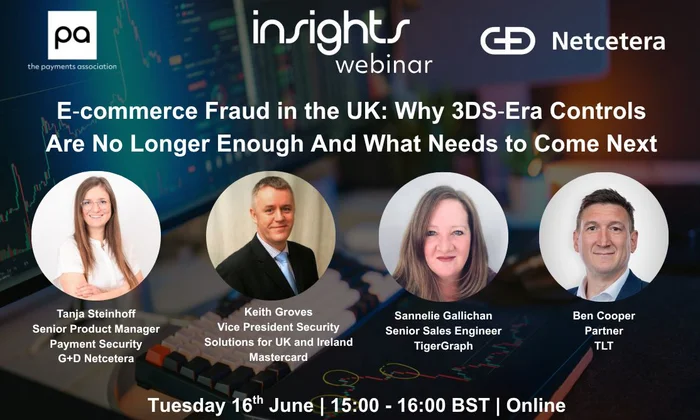
This free on-demand webinar with G+D Netcetera and The Payments Association UK explores why 3DS alone is no longer enough, and how banks can use earlier intervention, cross-channel intelligence and secure data sharing to make fraud prevention more proactive.
G+D Netcetera Becomes an Official AWS Partner, Strengthening Cloud-Based 3DS Solutions
Your Essential Introduction to Passwordless Authentication. Tired of password resets, phishing attacks, and frustrated customers? It's time to discover passkeys—the authentication technology that's making passwords obsolete.
Payment trends for 2026: digital identity wallets, network tokenisation, AI fraud prevention, VRPs, embedded finance and payment orchestration.
In our latest podcast episode, payment network expert Michael Schoch explains how Secure Remote Commerce (SRC) is creating new growth opportunities for domestic card networks.
This Tech Tribe episode gives a rare look into how advanced fraud prevention works when every second counts — and how the right expertise can turn a crisis into a controlled situation.
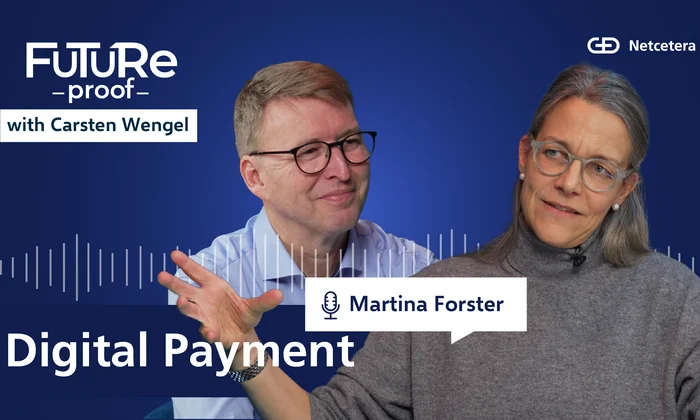
CEO Carsten Wengel sits down with Martina Forster, Portfolio Owner for Secure Digital Payments at G+D Netcetera, to explore the evolving world of digital payments: from 3-D Secure to instant payments, Big Tech, and digital identity.
Protecting the business and customers from invisible threats
Make Instant Payments a success with G+D Netcetera, as your strategic partner
Remember the last time you abandoned a purchase because you couldn’t find your card? How much time, energy, and mood did you waste filling in the requested information? Ultimately, you just left your purchase because it was too time-consuming, data-consuming, and energy-consuming. Sound familiar? That’s exactly why Click to Pay was created. In this episode with Suzana Kordumova Nikolova, we explore what makes Click to Pay different from Apple Pay and Google Pay, how it enhances security, and why businesses adopt it.
Passwords are becoming a thing of the past. Passkeys deliver a safer, faster, and more seamless way to log in and approve payments. Payment expert Nakjo Shishkov explains how passkeys, 3DS, Click to Pay, and FIDO authentication set new standards for secure digital experiences. Learn how passkeys work, why they improve security, and how they drive better user journeys and higher conversion rates.
Wach the Click to Pay webinar featuring G+D Netcetera, Worldline, and Visa experts.
Maximizing Trust and Efficiency: G+D Netcetera expands ISAE 3402 certification to cloud services