G+D Netcetera manages 1.4 billion tokens
Payment tokenization as prerequisite in e-commerce

Unifies card, A2A, online banking, wallet and instant-payment signals into one real-time customer risk view inside your organization, so a detection in one channel strengthens every other decision.
Shares high-risk signals across banks and PSPs in near real time, so a fraud pattern caught at one institution stops it from reappearing, clean, at the next one.
Real-time scoring, privacy-by-design, API-first integration and hybrid machine-learning plus rules, all working together to keep pace with instant payments.

One risk view across card, A2A, online banking and wallet replaces separate channel dashboards, so a signal in one channel strengthens every decision your fraud team makes.

Scoring runs in milliseconds, built for instant-payment rails where funds clear before a manual review could ever start, let alone finish in time.

API-first design connects to your existing fraud orchestration and case management systems. No rip-and-replace, no new team to hire, no lost investment.
Every channel, e-commerce, mobile banking, e-banking, wallet, publishes activity signals such as suspicious devices, stolen credentials, mule patterns and rapid limit changes.
Other channels in the same organization consume these signals in real time, so a detection anywhere strengthens risk decisions everywhere.
Fraud alerts, IBANs, device and merchant indicators are shared across banks and PSPs in near real time, aligned with EU-wide feeds such as FRIDA and Banque de France MISP as well as domestic platforms.
A detection at one bank becomes protection at the next, before the same fraudster can reuse the same trick twice.
A central hub aggregates signals from every channel and external source, then returns one cross-channel risk score.
Hybrid machine-learning and rule-based models keep that score current as new fraud patterns keep appearing across the wider network, not just inside your own organization's four walls.


A stolen password or hijacked device is flagged the moment it appears, before it reaches a payment, wherever the customer banks with you across channels.

A complete risk picture means genuine payments are less likely to be blocked by rules that were only ever built for a single channel in isolation.

Cross-bank alerts stop the same mule, device or merchant from reaching a customer again at a completely different institution just days later.
Article 83a will require PSPs to share fraud and risk data with other PSPs and competent authorities in near real time, enabling proactive blocking before a transaction completes.
Provisional political agreement was reached in November 2025, with the obligation expected to take effect around 2028, and the groundwork needs to start well before that date.
SCT Inst and 24/7 real-time settlement schemes now clear funds in under ten seconds flat.
Once a payment is authorized, it cannot be recalled, so detection has to happen before authorization clears, not after the money and the fraudster are both already gone for good, well beyond any hope of recovery.
G+D Netcetera runs 3DS authentication for a major share of European card volume and serves thousands of financial institutions across the continent.
That reach on both the issuing and acquiring side, in one governance model, is what makes the cross-organization layer possible in the first place, not just a roadmap promise.
Only fraud signals: suspicious devices, stolen credentials, mule patterns, compromised IBANs and behavioural anomalies. Customer data itself is never shared between institutions. The platform follows GDPR-compliant anonymisation and the purpose-limitation principle set out in the PSR/PSD3 proposal, so shared signals can only ever be used to prevent fraud, and a recipient PSP is bound by confidentiality obligations on what it receives.
The platform is API-first and connects to the fraud orchestration and case management systems you already run today, without disruption. Most banks start with a single rail, often 3DS or card-not-present, then add A2A, instant payments and wallets in their own order of priority as confidence and integration effort allow. There is no need to replace what already works, and no forced migration timeline to follow.
It starts with a half-day value workshop to map your exposure and priorities against your own volumes. From there, most institutions onboard one gateway first, usually e-commerce, within two to four weeks, then expand across rails over the following months as each new rail strengthens detection in all the others, building toward full cross-channel and cross-organization participation across the whole organization.
Risk-based authentication for card-not-present transactions, the natural starting point for your first cross-channel rail.
1st in Europe, 2nd globally EMVCo-approved. G+D Netcetera 3DS Server SaaS: PCI 3DS + PCI DSS certified, 10+ card networks. Stop fraud. Keep conversion.
Real-time case investigation and fraud marks that feed directly into your cross-channel risk view.
Payment tokenization as prerequisite in e-commerce
First-party misuse is now the world’s leading type of fraud, yet it is almost impossible to spot at checkout. Discover why friendly fraud is rising, what it costs the payments industry, and how better data sharing could help distinguish genuine disputes from deliberate abuse.
G+D Netcetera wins two Juniper Awards 2026 for fraud prevention and digital wallets, as banks rethink their systems landscape for future payments
3DS and SCA are working as designed. So why is UK payment fraud still rising?
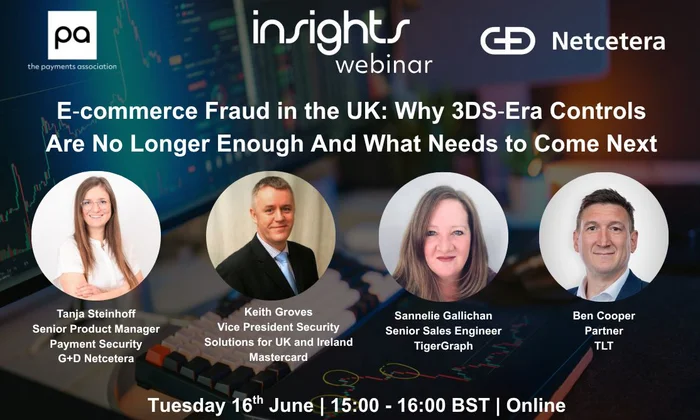
This free on-demand webinar with G+D Netcetera and The Payments Association UK explores why 3DS alone is no longer enough, and how banks can use earlier intervention, cross-channel intelligence and secure data sharing to make fraud prevention more proactive.
G+D Netcetera Becomes an Official AWS Partner, Strengthening Cloud-Based 3DS Solutions
Your Essential Introduction to Passwordless Authentication. Tired of password resets, phishing attacks, and frustrated customers? It's time to discover passkeys—the authentication technology that's making passwords obsolete.
Payment trends for 2026: digital identity wallets, network tokenisation, AI fraud prevention, VRPs, embedded finance and payment orchestration.
In our latest podcast episode, payment network expert Michael Schoch explains how Secure Remote Commerce (SRC) is creating new growth opportunities for domestic card networks.
This Tech Tribe episode gives a rare look into how advanced fraud prevention works when every second counts — and how the right expertise can turn a crisis into a controlled situation.
CEO Carsten Wengel sits down with Martina Forster, Portfolio Owner for Secure Digital Payments at G+D Netcetera, to explore the evolving world of digital payments: from 3-D Secure to instant payments, Big Tech, and digital identity.
Protecting the business and customers from invisible threats
Make Instant Payments a success with G+D Netcetera, as your strategic partner
Remember the last time you abandoned a purchase because you couldn’t find your card? How much time, energy, and mood did you waste filling in the requested information? Ultimately, you just left your purchase because it was too time-consuming, data-consuming, and energy-consuming. Sound familiar? That’s exactly why Click to Pay was created. In this episode with Suzana Kordumova Nikolova, we explore what makes Click to Pay different from Apple Pay and Google Pay, how it enhances security, and why businesses adopt it.
Passwords are becoming a thing of the past. Passkeys deliver a safer, faster, and more seamless way to log in and approve payments. Payment expert Nakjo Shishkov explains how passkeys, 3DS, Click to Pay, and FIDO authentication set new standards for secure digital experiences. Learn how passkeys work, why they improve security, and how they drive better user journeys and higher conversion rates.
Wach the Click to Pay webinar featuring G+D Netcetera, Worldline, and Visa experts.
Maximizing Trust and Efficiency: G+D Netcetera expands ISAE 3402 certification to cloud services